Short · Crypto security
How did hackers drain Binance without the key?
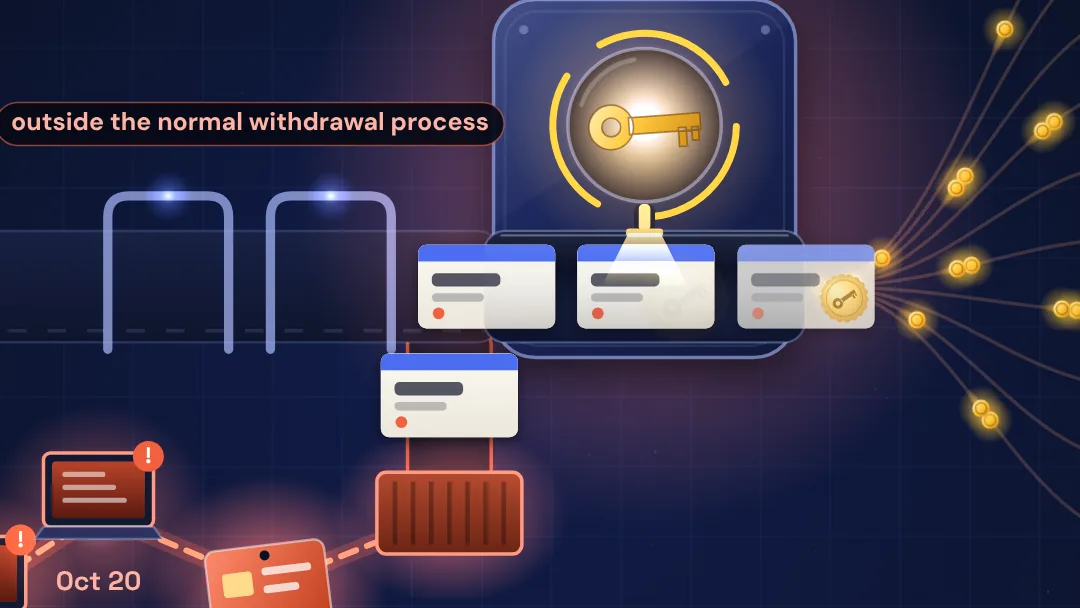
Binance says hackers moved about $6.34 billion out of its hot wallets on October 29, and that it found no sign a private key leaked. A hot wallet stays online, and its key is kept inside a service that signs requests all day. A signature only proves the key said yes, not that anyone meant it. Binance says hacked engineer computers led, in steps, to that signing service, so unauthorized requests got genuine signatures, and the drain took under four hours. In the model, a check at the signer fixes it: a request with no matching customer withdrawal gets no signature.
Opens Signed, Not Meant. Change the same thing yourself.
Transcript
Hackers moved over six billion dollars out of Binance. Binance says it found no sign the key leaked. So how? A hot wallet stays online, so withdrawals go out fast. Its key is kept inside a service that signs requests all day. But a signature only proves the key said yes. Not that anyone meant it. Binance says hacked engineer computers led, in steps, to that service. Unauthorized requests got genuine signatures. The drain took under four hours. Now add a check at the signer: no matching withdrawal, no signature. The attackers' requests bounce. A key is only as safe as whatever can ask it to sign. Follow for more explainers like this.
Learn more
Learn more about the Binance hack
This model shows why a genuine signature isn’t proof anyone meant it. The guide adds the route Binance describes, the numbers, frozen versus covered versus recovered, and where the model stops.
- Topic guideHow were $6 billion stolen from Binance with genuine signatures?The signing service, the route in, the four-hour drain, EIP-7702 delegations and the check that would bounce them.
- Interactive demoTHE CONSTRUCT — Bitcoin vs. The Quantum MachineThe elliptic-curve math behind the keys and signatures Bitcoin uses.by Brad Mills · Best on a larger screen
 JournalHow did hackers drain Binance without the key?Binance says attackers moved about $6.34 billion out of its hot wallets without a leaked key. A signature proves a key said yes, not that anyone meant it.