Computer Science · Interactive demo
How did hackers drain Binance without the key?
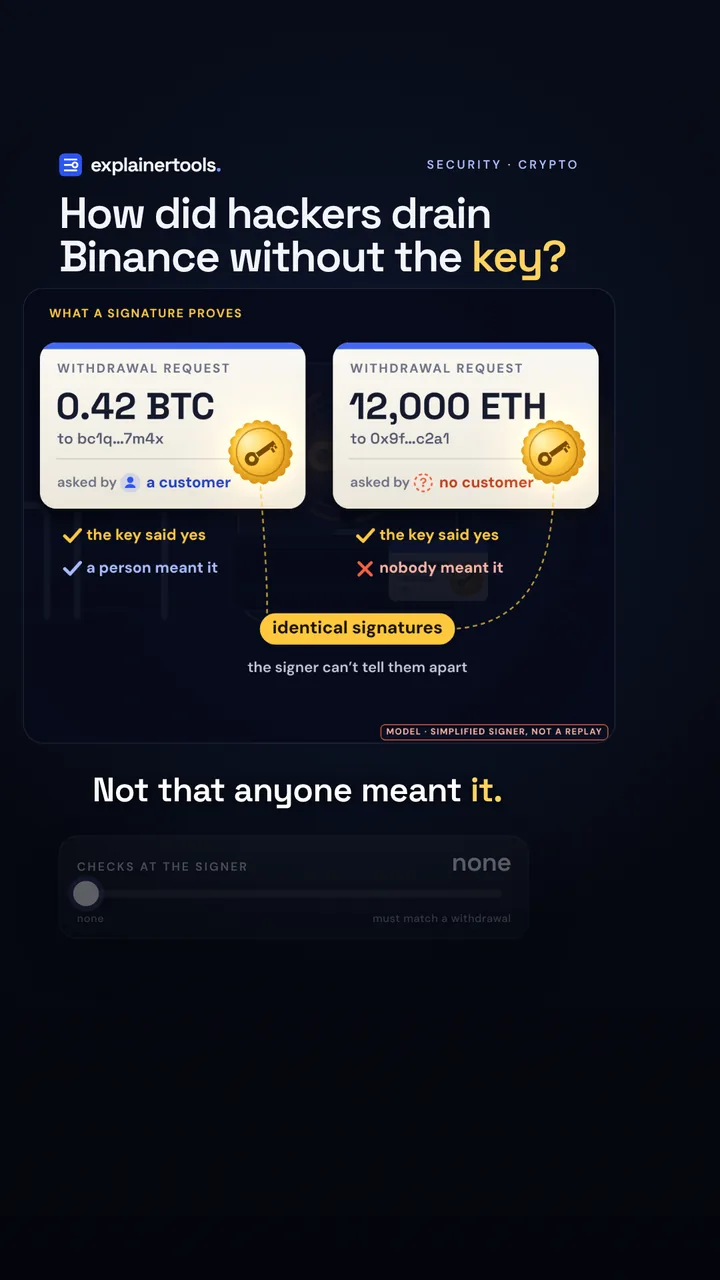
Add a check at an exchange’s signing service and watch an attacker’s requests bounce. A genuine signature isn’t proof anyone meant it.
Created by ExplainerTools.
About this explainer
- Made by
- ExplainerTools
- Format
- Interactive demo
- Subject
- Computer Science
- Where it runs
- Plays here
- Full tool
- Open the tool page
- Published
- Added to collection
- crypto
- security
- digital signatures
- hot wallets
- Binance
How the model works
Binance says hackers moved about $6.3 billion out of its hot wallets on October 29, and it found no sign that a private key leaked. Every one of those withdrawals carried a genuine signature. How did hackers drain Binance without the key?
- Money in the hot wallet$100M → $10B
- Checks at the signernone → a person approves
- How far the attacker gotone laptop → the records
A toy exchange with one hot wallet and three dials (money kept hot, checks at the signer, how far the attacker got); its rates and 4-hour stop are illustrative. Binance figures from Binance’s Nov 3 findings, Elliptic and TRM Labs. Not a replay of the attack, and not a claim about which checks Binance’s signer ran.
Model notes and sources
Model. A toy exchange with one hot wallet. Its key is kept inside a signing service that signs any well-formed request it is handed (Binance’s hot wallet used MPC, a key split into shares; the turning gold arcs stand for them). Customers’ requests reach the signer through the normal withdrawal process; an attacker’s requests reach it only if the attacker controls something that can talk to the service. Checks at the signer: none (it signs anything well formed); amount limits (no single big request, at most $0.25B an hour); must match (each request must match a customer withdrawal in the exchange’s records); + a person (anything over $1M also needs a person to approve it through a separate channel). How far the attacker got: one laptop, a deployment token, the signing service, or the withdrawal records too. The attacker sends requests as fast as they are signed, and the exchange stops the drain after 4 hours. Could leave in 4 hours = min(hot wallet, rate × 4 h), where the rate is unlimited with no check, $0.25B an hour under limits, and about $0.06B an hour (one $1M request a minute) when a person approves the big ones. Stablecoin part = 54% of that: the stablecoin share of the Binance haul in Elliptic’s count ($3.46B of $6.43B), the part an issuer can freeze (in the Binance case about $0.79B of stablecoins were swapped before the freezes landed, Elliptic says, so “freezable” is an upper bound). Customer withdrawals assumes customers take out about $1B a day, so a smaller hot wallet waits on refills from cold storage. These dials and rates are illustrative; only the Binance figures below are sourced.
What Binance says happened. In its November 3 findings, Binance says attackers compromised several engineers’ computers (a tampered Homebrew download in June, a fake job interview in September, and, on October 20, an internal AI tool used to take over other engineers’ computers), took a container-deployment token, and deployed a container that reached its internal wallet-signing service. Transactions were started through that service outside the normal withdrawal process, so they carried genuine signatures; on Ethereum, the roughly 50 signed requests were EIP-7702 delegations that handed hot-wallet accounts to an attacker-controlled contract, which then swept them. Binance says it found no evidence that private keys leaked. The drain ran from about 20:05 to 23:56 UTC on October 29 across about 10 chains (TRM Labs). Binance puts the impact at about $6.34B (Elliptic counts $6.43B, TRM Labs $6.36B), and about $2.85B was frozen or intercepted. Binance says it is covering the loss from its own funds and had replenished about 98% of impacted assets: that is Binance paying, not the stolen coins coming back. Frozen is not recovered either; Circle, for example, can block an address from moving USDC but cannot reverse a completed transfer. The FBI, the Secret Service and IRS-CI attribute the theft to North Korea’s TraderTraitor group; North Korea denies it.
Why a genuine signature isn’t enough. A digital signature is a mathematical proof that whoever controls a key approved a transaction. It cannot say whether a person meant it, so a key is only as safe as whatever can ask it to sign. The fix in the film, a check where the key lives that each request matches a real withdrawal, is our model of a common defence; it is not a claim about what Binance’s signer did or didn’t check, which Binance has not published.
The pictures. Everything on the stage is drawn in code: the vaults, the signer, the requests (their amounts and addresses are made up), the coins and the route. The film’s drain curve follows the reported times (first transfers at 20:05, the large Ethereum sweep about 20:20–20:24, most chains within about half an hour, a smaller second wave 23:05–23:56) with a simplified shape. The one real clip in the film, on “Binance says it found no sign the key leaked”, is 3.5 seconds of Binance co-CEO Richard Teng’s own incident-update video (X, @_RichardTeng, October 30, 2026), shown picture only and credited on screen.
Limits. Real exchanges run many hot wallets and layered controls (risk engines, rate limits, multi-party approval, monitoring); this tool keeps one wallet and three dials. An attacker who controls both the records and the approvals beats any check that trusts them, and limits only slow a drain. Detection, freezes and recovery are left out of the 4-hour figure.
Sources: Binance, 29 October 2026 Security Incident: Initial Findings and Response Update (Nov 3, 2026) and Security Incident Update #2 (Oct 30); TRM Labs, North Korea steals USD 6.36 billion from Binance; Elliptic via Bitbo, 44% of $6.43B Binance hack loot now frozen; SOCRadar, Binance hack: $6.3B hot wallet theft (timeline); TechCrunch, Binance resumes withdrawals; The Hacker News, FBI links TraderTraitor to the Binance heist; Binance Academy, Hot vs. cold wallet; bitcoin.org, How Bitcoin works (signatures); Richard Teng, An update on the security incident (X, Oct 30, 2026; film footage); Circle, Stablecoin blocklisting process.
An ExplainerTools Original. Attack route as Binance described it on November 3, 2026; figures from Binance, Elliptic and TRM Labs.
Watch it move
- How did hackers drain Binance without the key?49-second Short
Explore interactive ideas in space, science, math, and more. Try a demo, read an interactive article, watch a short video, and follow what makes you curious.
New Originals
Change one thing and see why.
The three newest models, each with a short film. Watch the question, then play with the answer.
Follow your curiosity
A collection of small doors into big ideas.
Format
Swipe or scroll for more formats →
Subject
Swipe or scroll for more subjects →
Topic
Swipe or scroll for more topics →
Sort by
Rankings count activity here on ExplainerTools. Newest means added to this collection.
Loading collection…
Make something click.
Made an explainer, or found one you love? Give it a place in the collection.